Adap DP-FL: Differentially Private Federated Learning with Adaptive Noise
Published 29 Nov 2022 in cs.LG, cs.CR, and cs.DC | (2211.15893v1)
Abstract: Federated learning seeks to address the issue of isolated data islands by making clients disclose only their local training models. However, it was demonstrated that private information could still be inferred by analyzing local model parameters, such as deep neural network model weights. Recently, differential privacy has been applied to federated learning to protect data privacy, but the noise added may degrade the learning performance much. Typically, in previous work, training parameters were clipped equally and noises were added uniformly. The heterogeneity and convergence of training parameters were simply not considered. In this paper, we propose a differentially private scheme for federated learning with adaptive noise (Adap DP-FL). Specifically, due to the gradient heterogeneity, we conduct adaptive gradient clipping for different clients and different rounds; due to the gradient convergence, we add decreasing noises accordingly. Extensive experiments on real-world datasets demonstrate that our Adap DP-FL outperforms previous methods significantly.
The paper introduces an adaptive mechanism that tailors gradient clipping and noise scale reduction based on model convergence to improve privacy-utility trade-offs in federated learning.
The paper’s methodology leverages differential privacy by dynamically adjusting noise scales and clipping thresholds to mitigate privacy risks under heterogeneous client conditions.
Experimental results on MNIST and FashionMNIST demonstrate significant improvements in model accuracy and reduced privacy budget usage compared to existing DP-FL methods.
Adap DP-FL: Differentially Private Federated Learning with Adaptive Noise
The paper "Adap DP-FL: Differentially Private Federated Learning with Adaptive Noise" introduces a new approach to enhance privacy in federated learning (FL) systems through adaptive noise mechanisms via differential privacy (DP). The Adap DP-FL scheme augments traditional federated learning by tailoring both gradient clipping and noise scales adaptively, addressing the heterogeneity and convergence behavior of model parameters.
Federated Learning and Differential Privacy
Traditional FL allows multiple decentralized data holders to collaboratively train machine learning models without sharing raw data, using only parameter updates. Despite this, potential privacy risks persist, such as model inversion attacks that can exploit shared models to infer sensitive data (2211.15893). Differential privacy offers a theoretical framework to mitigate such risks by introducing random perturbations to data outputs, ensuring that no single data point significantly affects the model, thus preserving privacy while maintaining utility.
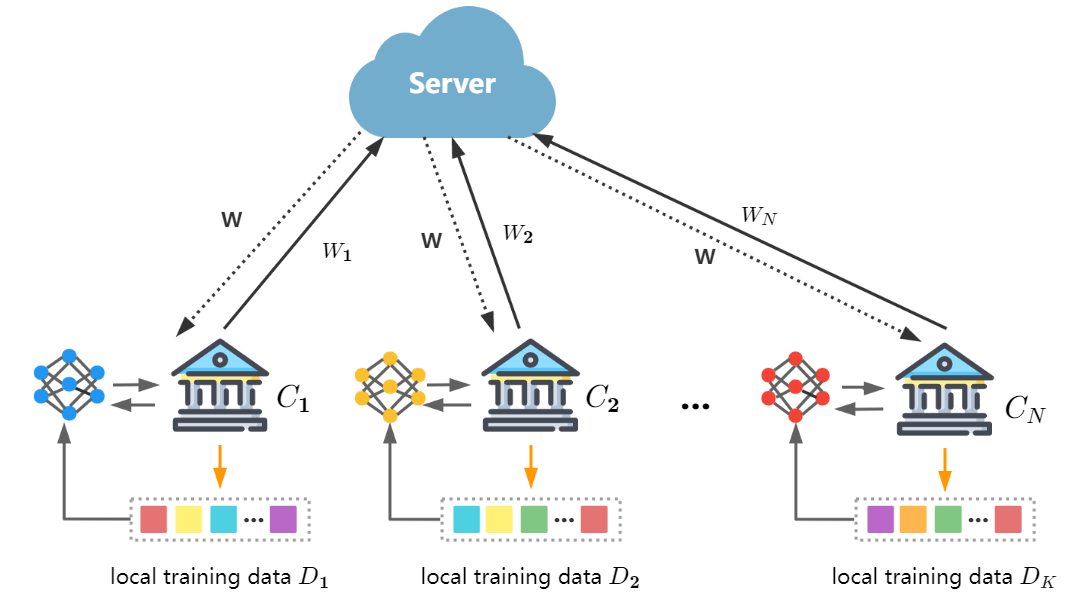
Figure 1: Federated Learning Model.
Adaptive Gradient Clipping
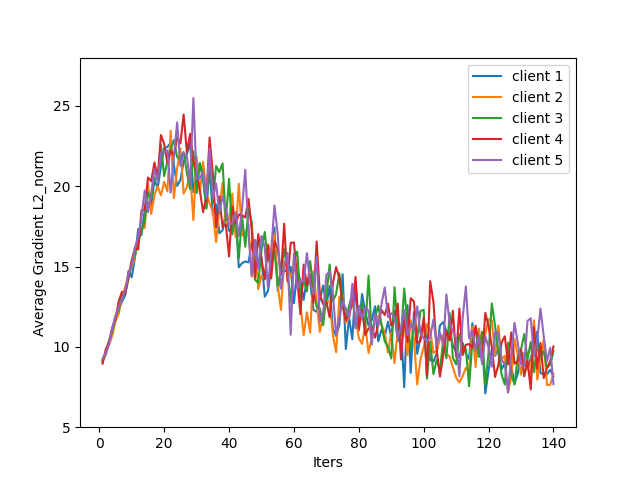
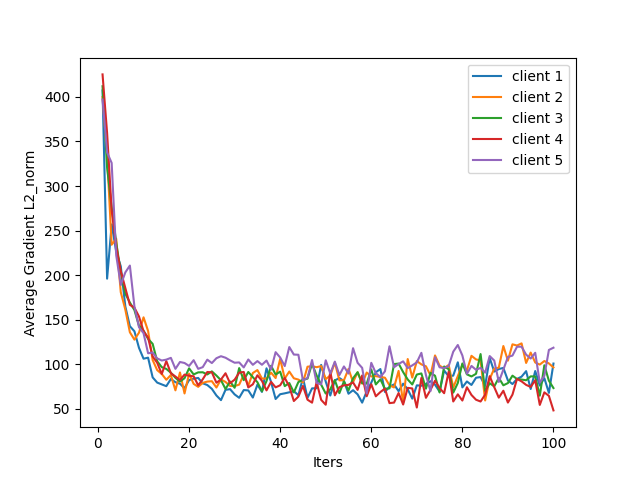
Adaptive gradient clipping addresses the inherent heterogeneity observed in the magnitude of gradients across different clients and rounds. Conventional methods suffer from fixed clipping thresholds, which fail to accommodate dynamic variations, potentially degrading model performance. Adap DP-FL introduces a mechanism that calculates clipping thresholds based on differentially private mean gradient norms from previous rounds, multiplied by a constant factor α:
This approach balances the bias and noise, optimizing the utility of the learned model.
Figure 2: The gradient l2-norm vary with different clients and different rounds in federated learning.
Adaptive Noise Scale Reduction
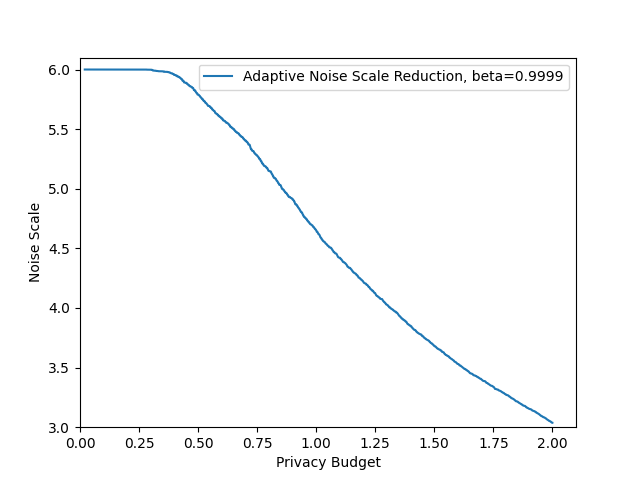
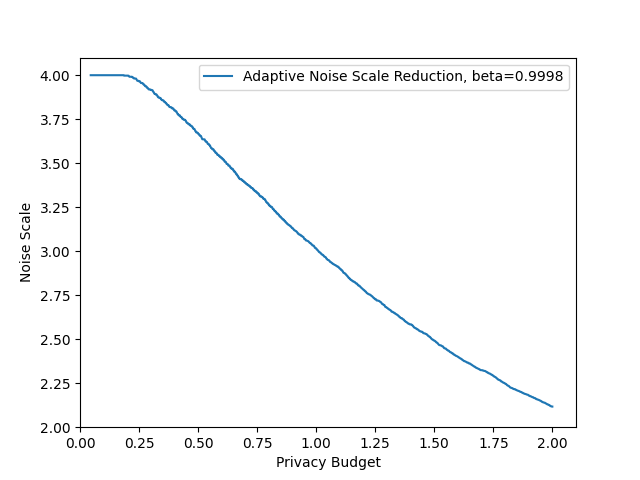
Adaptive noise scale reduction is implemented by decreasing the noise scale based on model convergence, as indicated by a sequence of validation loss reductions. When the validation loss decreases consecutively, indicating model stabilization, noise scales are reduced by a factor β, optimizing privacy budget allocation and improving model accuracy in later training stages.
Figure 3: The variation of noise scale σ for privacy budget in Adaptive noise scale reduction.
Implementation and Results
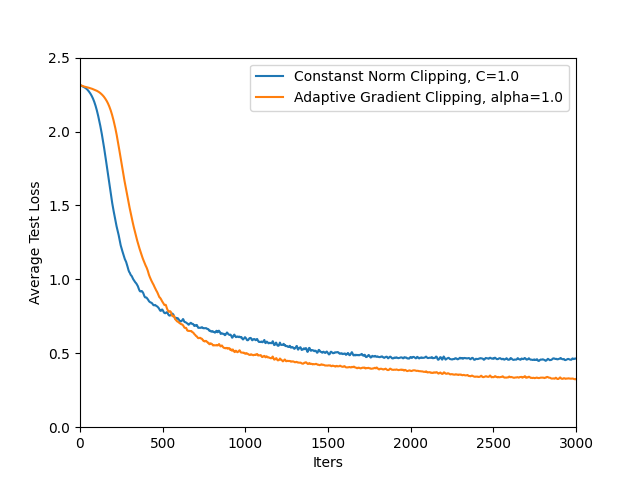
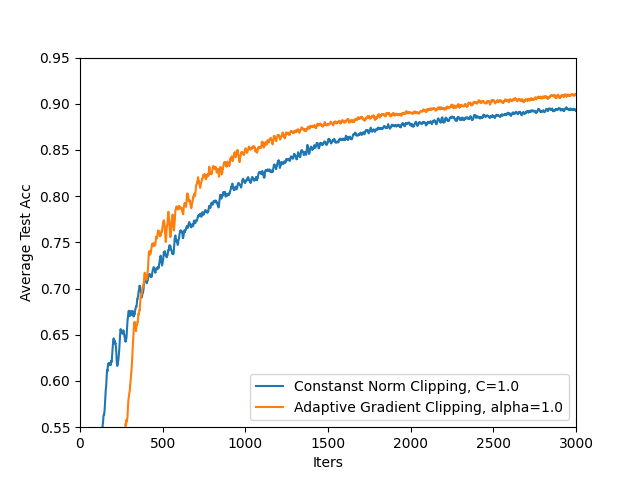
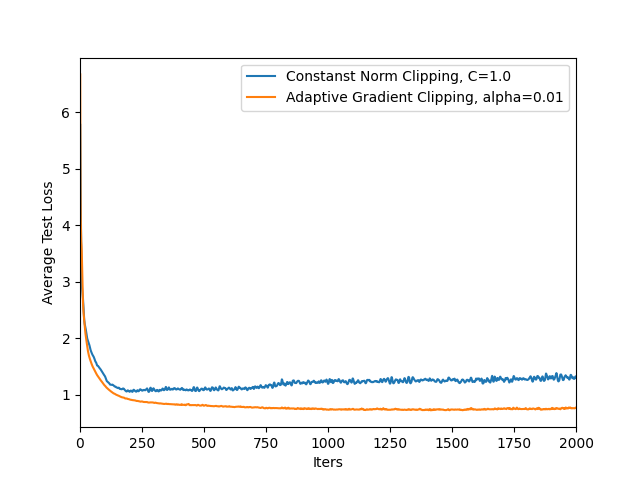
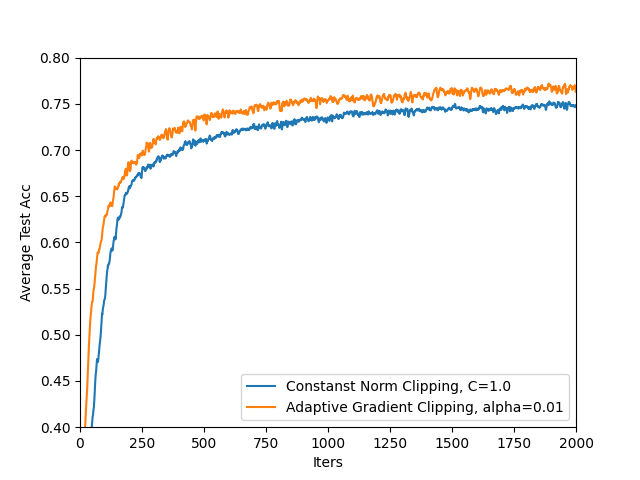
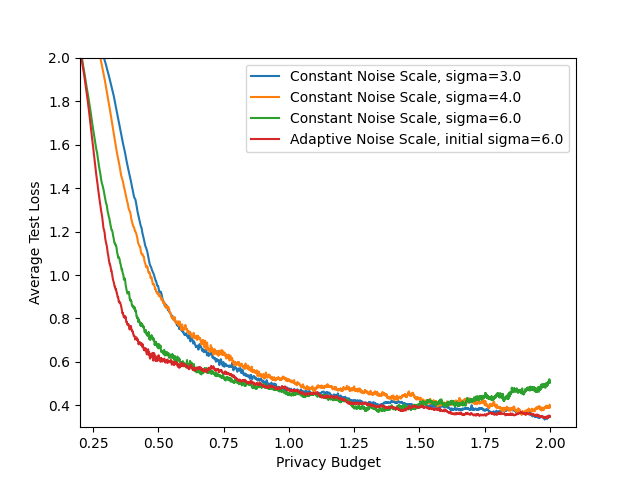
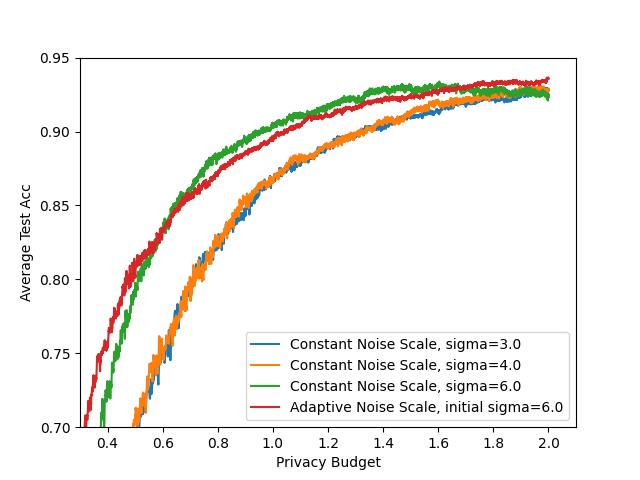
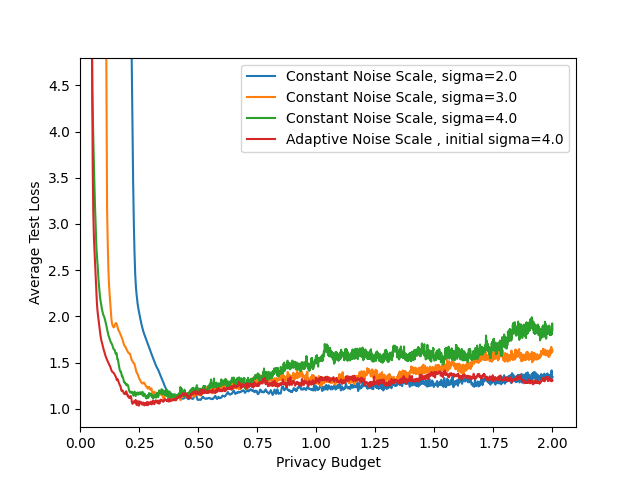
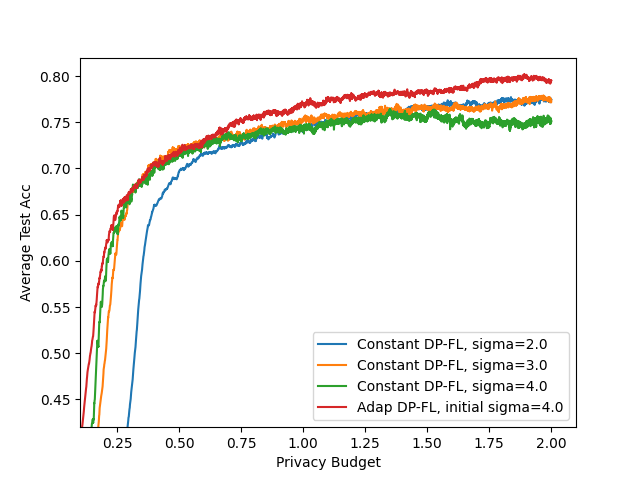
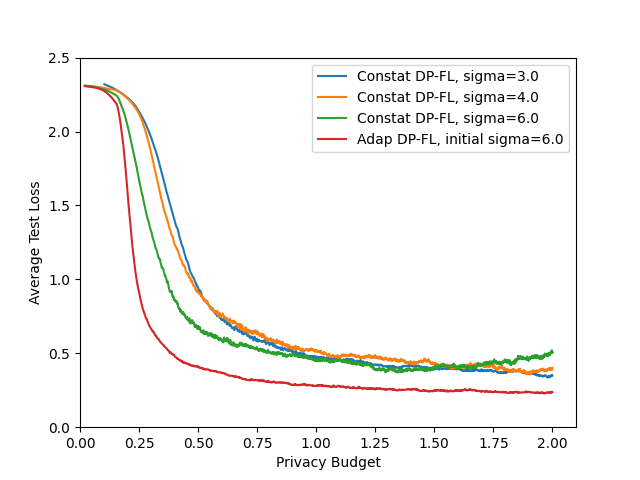
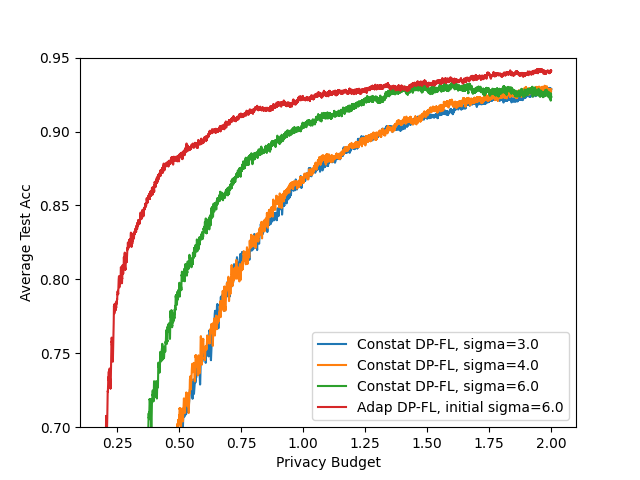
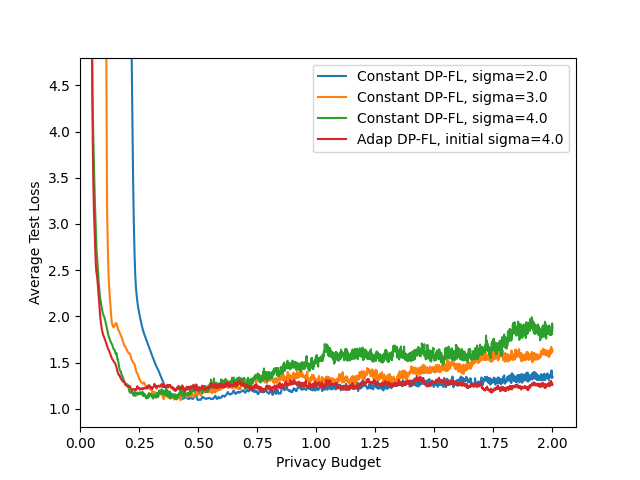
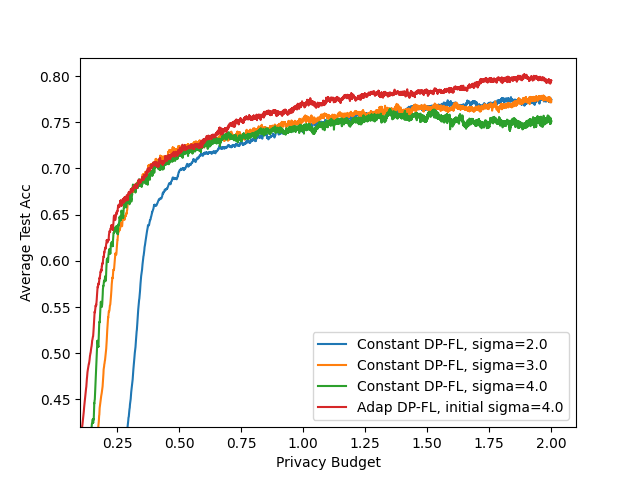
The Adap DP-FL method demonstrated significant improvements in model accuracy compared to existing DP-FL methods, using experiments on the MNIST and FashionMNIST datasets. The combination of adaptive gradient clipping and noise scale reduction facilitates better balance between privacy preservation and model performance, achieving higher accuracy while consuming lower privacy budgets.
Figure 4: Performance for adaptive gradient clipping method on MNIST dataset and FashionMnist dataset.
Figure 5: Performance for adaptive noise scale reduction method on MNIST dataset and FashionMnist dataset.
Figure 6: Performance for Adap DP-FL method on MNIST dataset and FashionMnist dataset. The clipping factor α=1.0 and noise reduction factor β=0.9999 for Adap DP-FL in MNIST datasets. The clipping factor α=0.01 and noise reduction factor β=0.9998 for Adap DP-FL in FashionMnist datasets.
Conclusion
The Adap DP-FL framework significantly enhances privacy in federated learning systems via adaptive mechanisms for gradient clipping and noise scale reduction, fostering improved model utility alongside robust privacy guarantees. The practical deployment of these techniques promises better optimization capabilities under constrained privacy budgets, highlighting the potential for future research into adaptive privacy-preserving architectures in federated learning environments.